CMMC draws from NIST SP 800-171 Revision 2, along with standards from the Department of Defense and the international security community, to protect Controlled Unclassified Information.
CMMC Update
The Department of War has suspended CMMC Phase 2 and launched a 60 day review of the program.
See what changed, what did not, and why most defense contractors should continue with business as usual.
Read the UpdateThe Edwards Approach to CMMC
Edwards supports organizations and professionals with CMMC readiness, cybersecurity consulting, authorized assessments, professional training, and approved educational materials.
Our cybersecurity team brings more than 50 years of combined experience working with cybersecurity standards, assessments, compliance requirements, and security best practices.
Cyber AB Authorized Roles
Authorized to conduct formal CMMC assessments for organizations seeking certification.
Learn what C3PAO means
Provides CMMC consulting and readiness support for organizations preparing for assessment.
Learn what RPO means
Authorized to deliver approved professional CMMC training, including education for CCP and CCA paths.
View ATP details
Authorized to develop approved educational materials used in professional CMMC training.
Learn what APP meansCMMC Fundamentals
A quick overview of the framework, who it affects, and how organizations prepare for CMMC requirements.
CMMC draws from NIST SP 800-171 Revision 2, along with standards from the Department of Defense and the international security community, to protect Controlled Unclassified Information.
CMMC requirements scale by level based on the contract and sensitivity of the information involved. Organizations must meet the requirements assigned to their applicable level.
CMMC requirements are now codified in 48 CFR. The Final Rule was published September 10, 2025, with the phased rollout beginning November 10, 2025.
CMMC affects the broader Defense Industrial Base, including approximately 300,000 contractors and subcontractors.
Approved Partner Publishers and Approved Training Providers support organizations and professionals preparing for CMMC requirements and certification.
Join Edwards aboard Celebrity Beyond for a week of CMMC education, community, practical insight, and CCP training at sea.
CMMC Readiness and Assessment
Understanding which CMMC requirements apply, how to prepare, and who is authorized to perform an official assessment can be difficult. Edwards helps organizations make sense of the process.
Understanding the Requirements
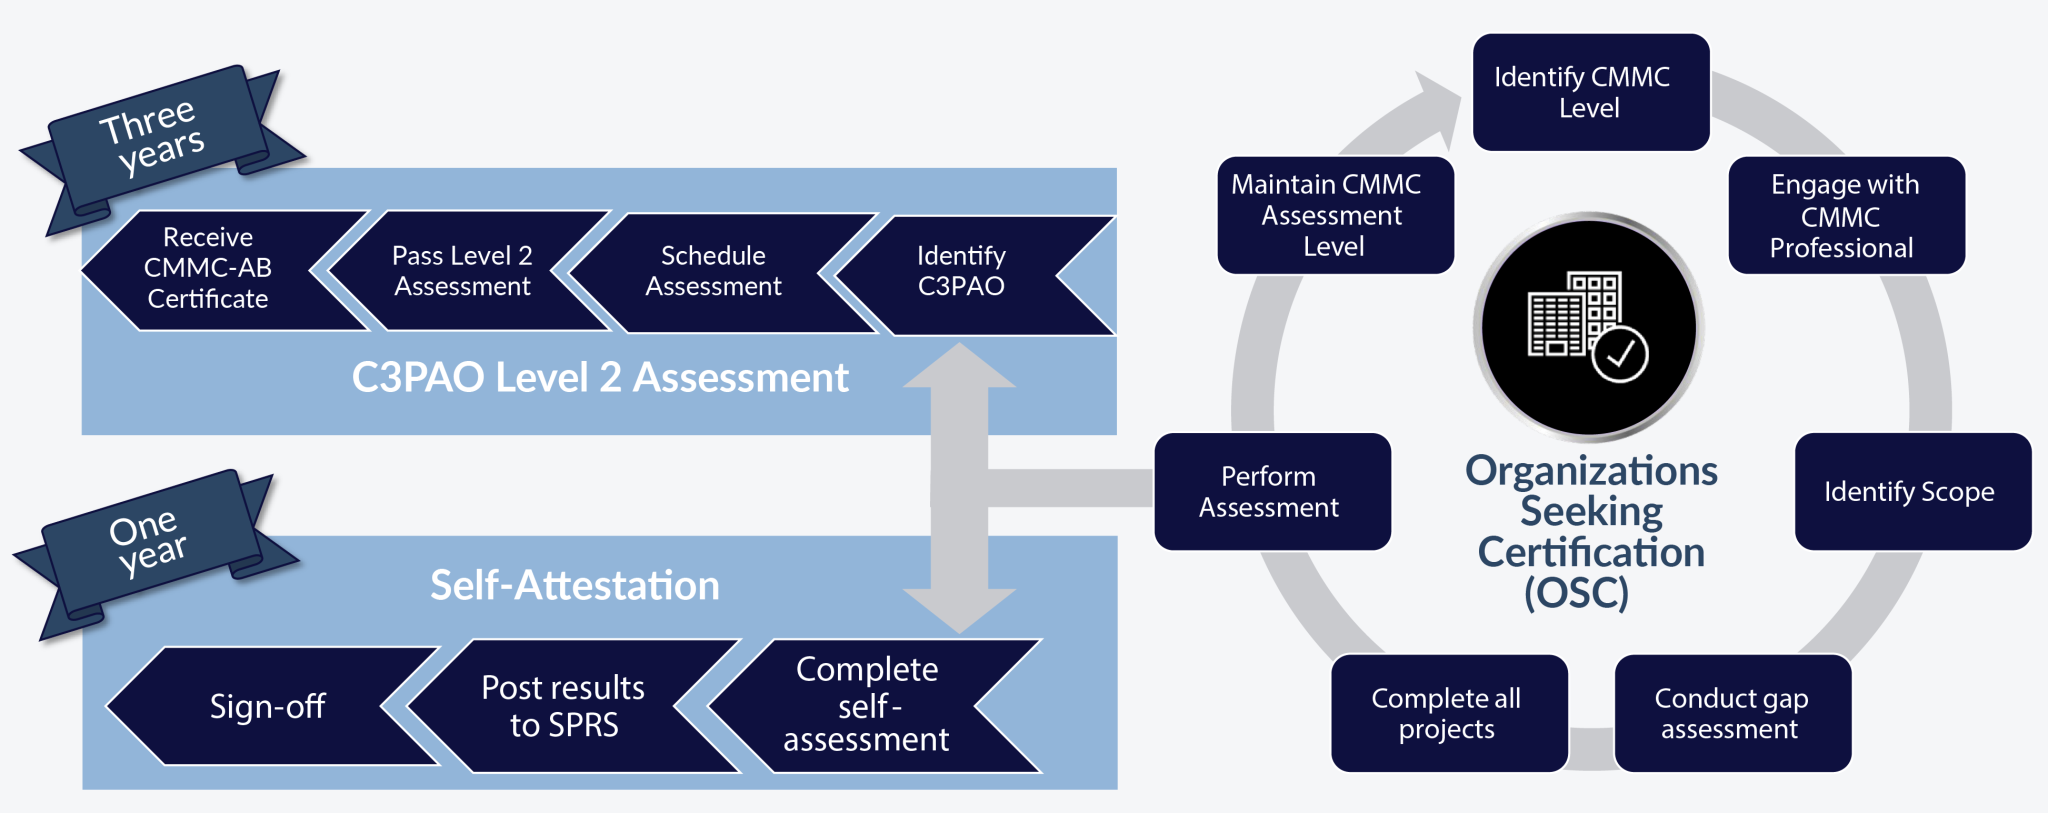
To work with the government, organizations must self attest to NIST SP 800-171 Rev 2 safeguards at CMMC Level 1 for Federal Contract Information (FCI), or meet Level 2 requirements for Controlled Unclassified Information (CUI) through self attestation when allowed by contract or through an independent assessment by a Certified Third Party Assessment Organization (C3PAO).
The Cyber AB created the Registered Provider Organization (RPO) designation to help Organizations Seeking Assessment and Organizations Seeking Certification identify consultants with verified CMMC expertise.
For official CMMC assessments, only C3PAOs are authorized to certify compliance with Level 2 requirements. If a government contract requires Level 3, a C3PAO assessment for Level 2 compliance is required before a DIBCAC Level 3 assessment.
The Edwards Approach
As both an RPO and a C3PAO, Edwards provides advisory CMMC Level 1 and Level 2 consulting services, including readiness assessments that help organizations identify gaps and develop a tailored CMMC action plan.
Edwards works with DoD suppliers to strengthen readiness, prepare for certification, and understand the CMMC maturity requirements that apply to their organization.
Edwards cybersecurity experts bring more than 50 years of combined experience assessing and interpreting standards, guidelines, and cybersecurity best practices. Edwards has conducted NIST SP 800-171 Rev 2 assessments since 2015 and was an early participant in the CMMC program ecosystem.
CMMC Training
Edwards provides approved CMMC training for professionals pursuing CCP and CCA credentials, along with Guided Learning, private classes, and training options for organizations with multiple learners.
The Cyber AB approved CMMC curricula for CCP and CCA.
CMMC Education & Certification
Find approved CMMC training for individuals and teams, professional certification paths, guided learning options, and approved course materials from Edwards.
Edwards provides CMMC training through live instruction, virtual learning, self paced courses, and Guided Learning. Guided Learning combines independent course work with live, instructor led study sessions.
Courses are designed to help learners understand CMMC, NIST SP 800-171, assessment expectations, and the practical responsibilities involved in protecting sensitive information.
Edwards provides approved professional training for learners pursuing roles such as Certified CMMC Professional (CCP) and Certified CMMC Assessor (CCA).
Edwards is both an Approved Training Provider and an Approved Publishing Partner in The Cyber AB ecosystem. Courses use approved CMMC training materials and are led by qualified instructors with practical CMMC experience.
Organizations do not have to send employees through training one at a time. Edwards can support private groups, multiple learners, live virtual instruction, Guided Learning, and programs tailored to an organization’s needs.
This can be useful when several people need the same foundation, a team is preparing for new responsibilities, or an organization wants employees learning together.
As an Approved Publishing Partner, Edwards develops CMMC training materials aligned with approved learning objectives. The content is informed by CMMC, NIST, assessment, consulting, and instructional design experience.
These materials support professional CMMC education delivered by Edwards and can also support other organizations operating within the approved training ecosystem.
Common CMMC Training Terms
Quick definitions for terms used throughout CMMC training.Understanding CMMC
The Cybersecurity Maturity Model Certification (CMMC) is a unified standard for strengthening cybersecurity across the Defense Industrial Base.
CMMC helps organizations protect sensitive information, understand cybersecurity expectations, and prepare for the contract requirements tied to Federal Contract Information and Controlled Unclassified Information.
The program is overseen by The Cyber AB and the Department of Defense. The Cyber AB supports a professional ecosystem of authorized organizations, instructors, publishers, consultants, and assessors who help companies prepare for and navigate CMMC.
C3PAO
RPO
ATP
APP
CMMC Levels Overview
CMMC organizes cybersecurity expectations into certification levels so organizations can understand what is required based on the information they handle and the work they perform.
The Cybersecurity Maturity Model Certification framework consolidates cybersecurity standards and best practices into three levels that range from foundational requirements to advanced assessment expectations. The level an organization must meet depends on contract requirements, the sensitivity of the information involved, and the nature of the work.
With CMMC now finalized under Title 48 CFR, these requirements are beginning to appear in Department of Defense contracts. November 10, 2025 marks an important milestone in that rollout, making preparation more urgent for organizations that want to compete for and retain DoD work.
Why this matters
CMMC Case Study
Harkins Builders needed a practical way to understand its CMMC environment, identify what mattered, and organize the work still ahead. Edwards helped turn a document heavy process into a clearer plan for assessment preparation.
Too much documentation and not enough clarity around scope, priorities, and where to begin.
Clearer scoping and a more usable foundation for cybersecurity work and CMMC assessment preparation.
Published in the ABC 2023 Tech Report
Harkins Builders + Edwards
CMMC Preparation
Preparing for CMMC starts with understanding your environment, identifying the requirements that apply, and finding the gaps that need attention before an assessment.
Review your current cybersecurity practices, systems, documentation, and CMMC scope.
Identify missing practices, incomplete documentation, and other issues that could affect readiness.
Prioritize the work, assign responsibility, and prepare your organization for the next stage of the CMMC process.
CMMC Support & Resources
Whether you are figuring out what requirements apply, preparing for an assessment, looking for CMMC training, or trying to understand what comes next, Edwards can help you find the right place to start.
Edwards supports organizations and professionals through CMMC readiness and consulting, authorized assessments, professional training, and practical CMMC education and resources.