Contact us

Cyber AB Authorized RPO & C3PAO

CMMC Consulting, Readiness & C3PAO Assessments

Get ready for CMMC with hands-on help from our consultants, then earn certification through an authorized C3PAOCertified Third-Party Assessment Organization: a company approved by The Cyber AB to perform official CMMC Level 2 certification assessments. assessment.

Talk to a CMMC Consultant

CMMC for Defense Contractors

What to Know About CMMC

Four questions every defense contractor asks before choosing CMMC help, answered in plain language.

The Cyber AB

What is CMMC?

CMMC is the Department of Defense program that checks whether contractors protect sensitive information. If you handle FCIFederal Contract Information: information about a government contract that isn't meant for the public, like pricing or delivery schedules. or CUIControlled Unclassified Information: sensitive government information, like technical drawings or specs, that must be protected by law. on a defense contract, you need to meet a CMMC level to win or keep that work.
The Pentagon

How does CMMC affect defense contractors?

CMMC requirements now appear in defense contracts, and primes pass them down to their subcontractors. You need to know what information you handle, which systems touch it, and which level applies. Waiting until an assessment is booked leaves little time to fix problems.

Edwards Performance Solutions

How can a CMMC consultant help?

A consultant shows you exactly where you stand and what to fix. Our team scopes your environment, runs a gap assessment, helps write your SSPSystem Security Plan: the document that describes your systems and how you meet each security requirement. Assessors read it first. and POA&MPlan of Action and Milestones: your written plan for fixing gaps, with owners and due dates., and works alongside your IT team until you're ready.

C3PAO credential

How do you choose a C3PAO?

Only a C3PAO authorized by The Cyber AB can perform an official Level 2 certification assessment. Make sure it's listed on the Cyber AB Marketplace, ask about its assessors' real-world experience, and confirm it can keep your information secure.

Cyber AB Authorized

Authorized in Four CMMC Roles

The Cyber AB authorizes companies for specific CMMC jobs. Edwards holds four, so you can get ready, get certified, and train your team with one trusted partner.

  • RPO

    Registered Practitioner Organization

    Our consultants are registered with The Cyber ABThe official accreditation body for CMMC. It authorizes the companies and people allowed to do CMMC work. to help you prepare for a CMMC assessment.

    CMMC readiness services
  • C3PAO

    Certified Third-Party Assessment Organization

    We can perform your official CMMC Level 2The level for companies that handle CUI. It has 110 security requirements, and most contracts require a C3PAO assessment every 3 years. certification assessment.

    C3PAO assessments
  • ATP

    Approved Training Provider

    We teach the official CCPCMMC Certified Professional: the entry-level CMMC certification and the first step toward CCA. and CCACMMC Certified Assessor: the certification required to perform official CMMC Level 2 assessments. certification courses, live online or at your own pace.

    CMMC training classes
  • APP

    Approved Publishing Partner

    We write approved CMMC course materials. In 2021, we were the first in the nationThe Daily Record reported in October 2021 that Edwards was the first company in the nation to earn the CMMC-AB’s approval for its CCP course materials. approved for CCP curriculum.

    CMMC bookstore

Check any credential yourself on the Cyber AB Marketplace (opens in a new tab), or see all Edwards credentials.

Why Edwards

Why Choose Edwards for CMMC?

We work on every side of CMMC. We train assessors, write the approved course materials, and perform official assessments. That inside knowledge goes into every consulting project, so you prepare for what assessors actually check.

  • CMMC Scoping

    We find exactly where your CUIControlled Unclassified Information: sensitive government information, like drawings or specs, that the law requires you to protect. lives and draw the smallest correct boundary, so you protect what matters without paying to secure everything.

    DoD Level 2 Scoping Guide (PDF, opens in a new tab)
  • Gap Assessments

    We review all 110 requirements in NIST SP 800-171The federal standard behind CMMC Level 2. It lists 110 security requirements for protecting CUI. the same way an assessor would, so nothing surprises you on assessment day.

    Readiness services
  • Remediation Planning & Support

    Every gap becomes a clear task with an owner and a due date in your POA&MPlan of Action and Milestones: your written plan for fixing gaps, with owners and due dates.. Then we work alongside your IT team until each one is closed.

    Harkins Builders case study (PDF, opens in a new tab)
  • Assessor-Level Insight

    Our team includes CCPsCMMC Certified Professionals: people trained and certified in CMMC requirements and assessment methods. and CCAsCMMC Certified Assessors: the people certified to perform official CMMC Level 2 assessments. who teach the official CMMC classes. You get advice from people who know what assessors look for.

    Meet our CMMC instructors
  • Cybersecurity Beyond CMMC

    CMMC often overlaps with NIST 800‑53, the NIST Cybersecurity Framework, and SOC 2An independent audit report that shows customers how a company protects their data.. We map the work once, so your effort counts across every framework you follow.

    Cybersecurity services

CMMC Compliance Case Study

How Harkins Builders found a clearer path to CMMC compliance

Harkins Builders needed a more practical way to prepare for CMMC. Edwards helped the team understand its environment and turn the remaining work into a plan it could actually use.

The challenge

A document-heavy process made it hard to see what mattered or where to start.

The result

Clear scoping gave Harkins a solid foundation for its cybersecurity work and assessment prep.

Read the CMMC case study

Published in the ABC 2023 Tech Report

Published case study Cover of the ABC 2023 Tech Report featuring the Harkins Builders CMMC case study Harkins Builders & Edwards

CMMC Consulting & Assessments

Talk to a CMMC Expert

Tell us where you are today. You don’t need your scope, level, or next step figured out. That’s what the first conversation is for, and it’s free.

  • Preparing for CMMC

    Scoping, gap assessments, remediation planning, and assessment prep.

  • Ready for a C3PAO assessment

    Get on our assessment calendar and map out your dates.

  • Not sure yet

    Choose “Not sure yet” in the form, and we’ll help you find the right next step.

Prefer to reach out directly?

Call us
443.561.1334
Consulting & assessments
info@edwps.com
CMMC training & classes
training@edwps.com
Current students & clients
CustomerSupport@EdwPS.com

Start Here

How can we help?

Share what you know, and a CMMC expert will follow up. We only use your details to respond to you. See our privacy policy.

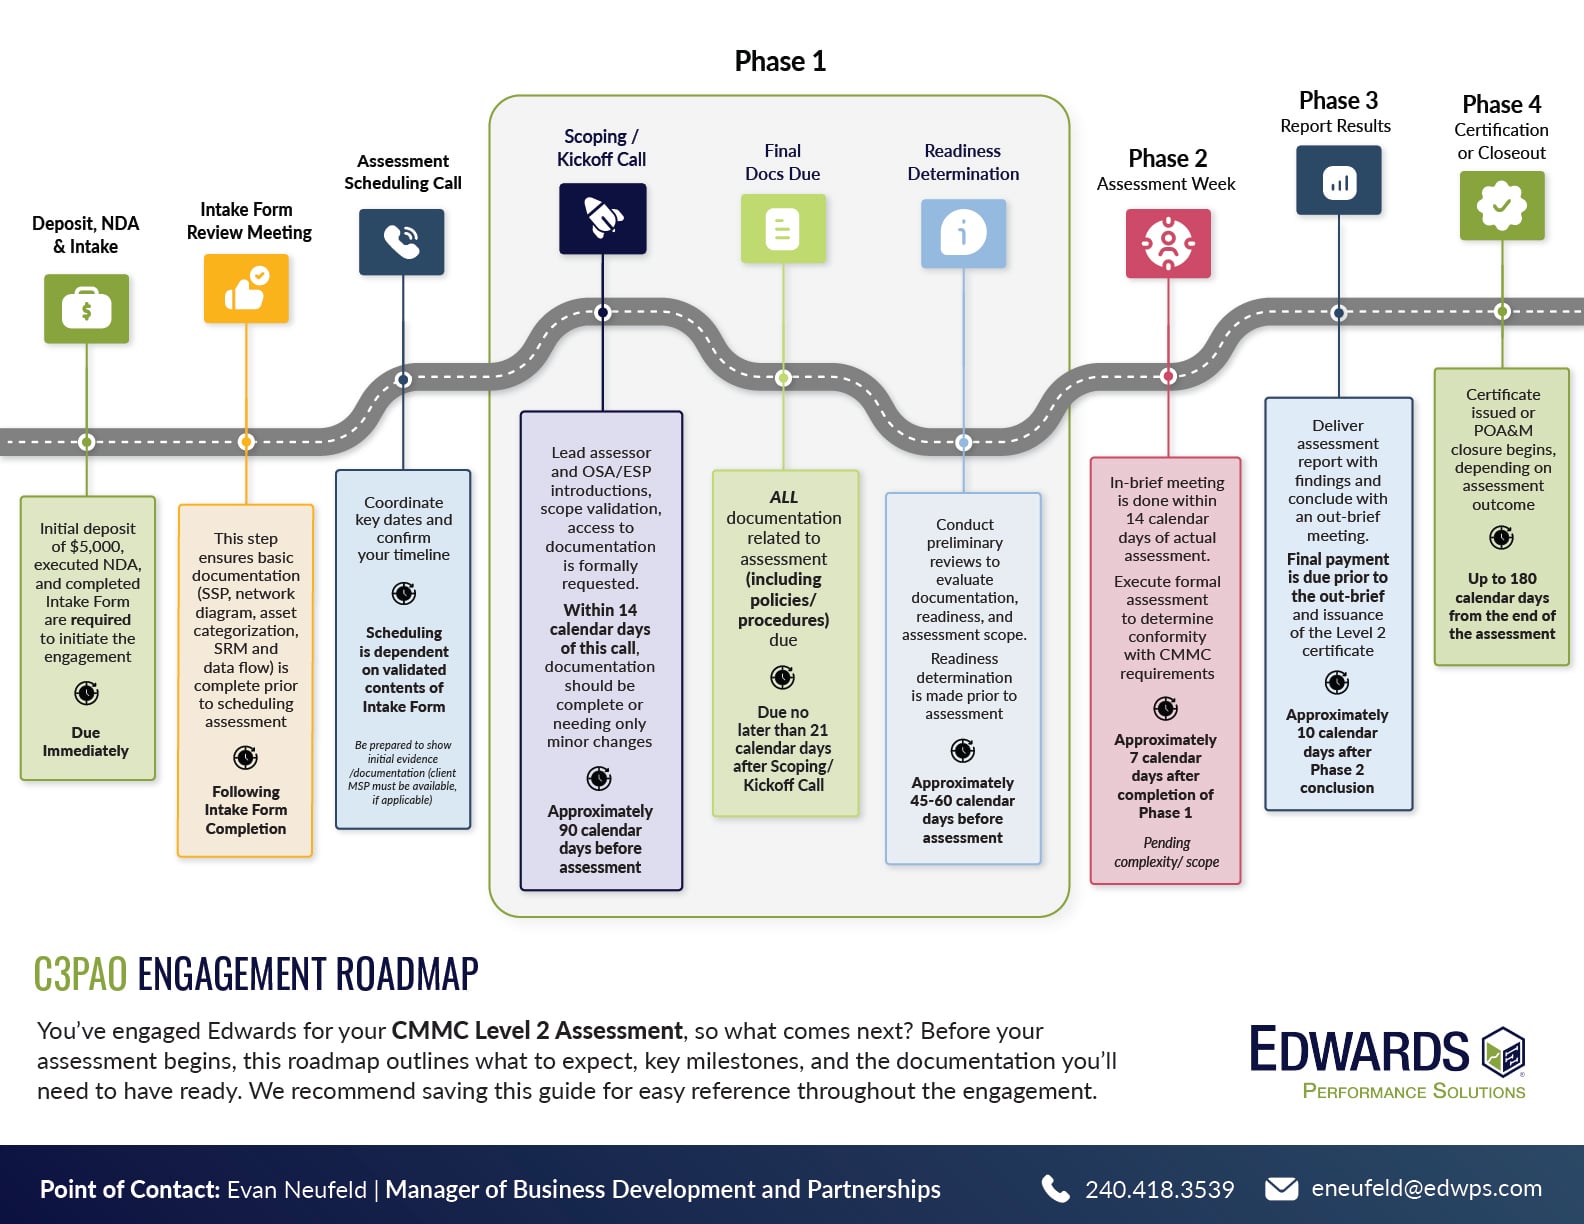
C3PAO Engagement Roadmap

Your CMMC Assessment Roadmap

Every Edwards C3PAO assessment follows the same clear path, from your first form to your Level 2 certificate. Here is the whole journey at a glance.

  1. Before you start

    Getting Started

    Right away

    • Deposit, NDA & intake form
    • Intake review meeting
    • Scheduling call
  2. Phase 1

    Readiness

    Starts about 90 days before assessment week

    • Scoping & kickoff call
    • Documents due within 21 days
    • Readiness check
  3. Phase 2

    Assessment Week

    About one week

    • In-brief meeting
    • Interviews & evidence review
    • Testing against all 110 requirements
  4. Phase 3

    Results

    About 10 days after

    • Assessment report
    • Out-brief meeting
  5. Phase 4

    Certification

    Right after, or within 180 days

    • Level 2 certificate issued
    • Or close small gaps under a POA&M
View the Full Roadmap Close the roadmap
Download it

When You Pass

Show Off Your CMMC Level 2 Status

Pass your Level 2 assessment with Edwards and you get a badge to use however you like. It shows your expiration date, and each year has its own color, so customers can tell at a glance that it’s current.

  • ASSESSED BY AUTHORIZED C3PAO EXP. NOVEMBER 2028 CMMC LEVEL 2 CERTIFIED
    2028Certified in 2025
  • ASSESSED BY AUTHORIZED C3PAO EXP. SEPTEMBER 2029 CMMC LEVEL 2 CERTIFIED
    2029Certified in 2026
  • ASSESSED BY AUTHORIZED C3PAO EXP. FEBRUARY 2030 CMMC LEVEL 2 CERTIFIED
    2030Certified in 2027
  • ASSESSED BY AUTHORIZED C3PAO EXP. DECEMBER 2031 CMMC LEVEL 2 CERTIFIED
    2031Certified in 2028

Your certification lasts three yearsA CMMC Level 2 certification from a C3PAO is good for three years from your final results. Your badge shows the month it ends., as long as your company completes its annual affirmationEach year, a senior company official must confirm in SPRS (the DoD’s Supplier Performance Risk System) that you still meet every requirement. each year.

  • Email Signatures

    Every message your team sends shows you’re certified.

  • Website and Proposals

    Add it to your capabilities page, bids, and RFP responses.

  • LinkedIn and Social

    Announce it to customers, primes, and partners.

Ready to earn yours? Talk to our C3PAO team about scheduling your Level 2 assessment.

Talk to Us About an Assessment

Sample badges shown. Your badge shows your company’s actual expiration date.

Assessment Timeline

How a CMMC Level 2 Assessment Works

A CMMC Level 2 assessment is an official review, done by an authorized C3PAO, that checks whether your company meets all 110 required security practices. Pass, and you can win and keep defense contracts that require Level 2 certification.

  • About 4 monthsfrom sign-up to certificate
  • About 1 weekfor the assessment itself
  • 3 yearsyour certificate stays valid

Click through an example: you sign up in early April

Mid-April in our exampleAbout 90 days before your assessment week

Kickoff call

Meet your lead assessor. Together we confirm exactly which people, systems, and locations are in scope, and you receive the official document request.

What you’ll need

  • Your main point of contact
  • Your MSPManaged Service Provider: an outside company that runs or supports your IT., if you use one
  • Any scope questions you have

Early May in our exampleWithin 21 days of your kickoff call

Documents due

Send every document tied to your assessment. By now, most should be finished or need only small changes.

What you’ll need

  • All policies and procedures
  • Your final SSPSystem Security Plan: the document that describes your systems and how you meet each security requirement.
  • Supporting evidence

Late May in our example45 to 60 days before your assessment week

Readiness check

We review your documents and scope and confirm you are ready. If something is missing, you find out now, with time to fix it, not during the assessment.

What you’ll need

  • Quick answers to our follow-up questions
  • Any missing documents

Mid-July in our exampleAbout one week, depending on your size

Assessment week

We open with an in-brief meeting. Then our assessors interview your team, review your evidence, and test your systems against all 110 Level 2 requirements.

What you’ll need

  • The right people available for interviews
  • Access to systems and evidence
  • Your MSP on call, if you use one

Late July in our exampleAbout 10 days after your assessment week

Results

We walk you through your report in an out-brief meeting. Pass, and your Level 2 certification is issued and recorded with the Department of Defense. If only a few eligible gaps remain, you receive conditional status and up to 180 days to close them under a POA&MPlan of Action and Milestones: your written plan for fixing gaps, with owners and due dates..

What you’ll need

  • Your final payment, due before the out-brief
  • A plan for yearly sign-off, which we explain
What you get when you pass

Dates are an example. Your real schedule depends on your size, scope, and how ready your documents are. See the full roadmap

What Assessors Check

CMMC Level 2 follows NIST SP 800-171A federal standard from the National Institute of Standards and Technology. It lists the security requirements for protecting CUI., which groups 110 requirements into 14 families. Tap any family to see what it covers, in plain English.

Access Control22 requirements

Only approved people and devices get into your systems, and each person sees only what their job requires. Screens lock after a period of inactivity.

Awareness & Training3 requirements

Everyone is trained to spot security risks, like phishing emails, and to report anything suspicious.

Audit & Accountability9 requirements

Your systems keep logs of who did what and when, and someone reviews them.

Configuration Management9 requirements

You keep an up-to-date list of your hardware and software, use secure settings, and control changes.

Identification & Authentication11 requirements

Every user has their own login, and multifactor authentication protects network and admin access.

Incident Response3 requirements

You have a plan to detect, report, and respond to security incidents, and you test it.

Maintenance6 requirements

System maintenance is approved and supervised, including any work done remotely.

Media Protection9 requirements

USB drives, laptops, and paper files that hold CUI are protected, encrypted, and destroyed properly.

Personnel Security2 requirements

People are screened before they get access to CUI, and access is removed when they leave.

Physical Protection6 requirements

Offices and equipment are locked down, visitors are escorted, and physical access is logged.

Risk Assessment3 requirements

You regularly assess risk and scan your systems for weaknesses, then fix what you find.

Security Assessment4 requirements

You check that your security works, keep your SSP current, and track fixes in a plan.

System & Communications Protection16 requirements

Data is protected where your network meets the outside world, and CUI is encrypted when it travels.

System & Information Integrity7 requirements

Flaws are fixed quickly, malicious code is blocked, and systems are watched for attacks.

Read all 110 requirements in NIST SP 800-171 (opens in a new tab)

What You Get When You Pass

  • Official Level 2 certification

    Your result is recorded with the Department of Defense, and your status appears in SPRSSupplier Performance Risk System: the Department of Defense database where contracting officers check your CMMC status..

  • The right to bid and keep work

    You can compete for, win, and keep defense contracts and subcontracts that require Level 2 certification.

  • Proof for your primes

    Prime contractors must confirm their subcontractors are certified. When they ask, you are ready.

  • Three years of coverage

    Your certificate lasts three years. A company leader confirms compliance once a year to keep it active.

Ready to get on our assessment calendar?

Tell us your contract deadline and we’ll map out your dates.

A $5,000 deposit reserves your assessment. You can pay online, by invoice, or through our accounting team. The final balance is due before your out-brief meeting.

CMMC Assessment FAQ

How long does a CMMC Level 2 assessment take?

Plan for about four months from sign-up to certificate. Your kickoff call happens about 90 days before assessment week, the assessment takes about a week, and results follow about 10 days later.

Who needs a C3PAO assessment?

Companies that handle Controlled Unclassified Information (CUI) on defense contracts that require CMMC Level 2 certification. Some Level 2 contracts allow a self-assessment instead, so check your contract or ask us.

How much does a CMMC Level 2 assessment cost?

The price depends on your company’s size and how much of your network is in scope. Ask us for a quote.

Can Edwards consult for us and assess us?

No. CMMC rules do not allow a C3PAO to assess a company it helped prepare. We can be your consultant or your assessor, and we will help you decide which fits. See our readiness services.

What happens if we don’t pass?

If only a few eligible requirements are not met, you receive conditional status and have 180 days to fix them. If bigger gaps remain, you fix them and schedule a new assessment.

How long is a CMMC certificate good for?

Three years. A senior company official must also confirm compliance every year in SPRS, the Department of Defense’s reporting system.